
15

Wichtige Fakten
- Keys never leave FIPS-validated HSMs
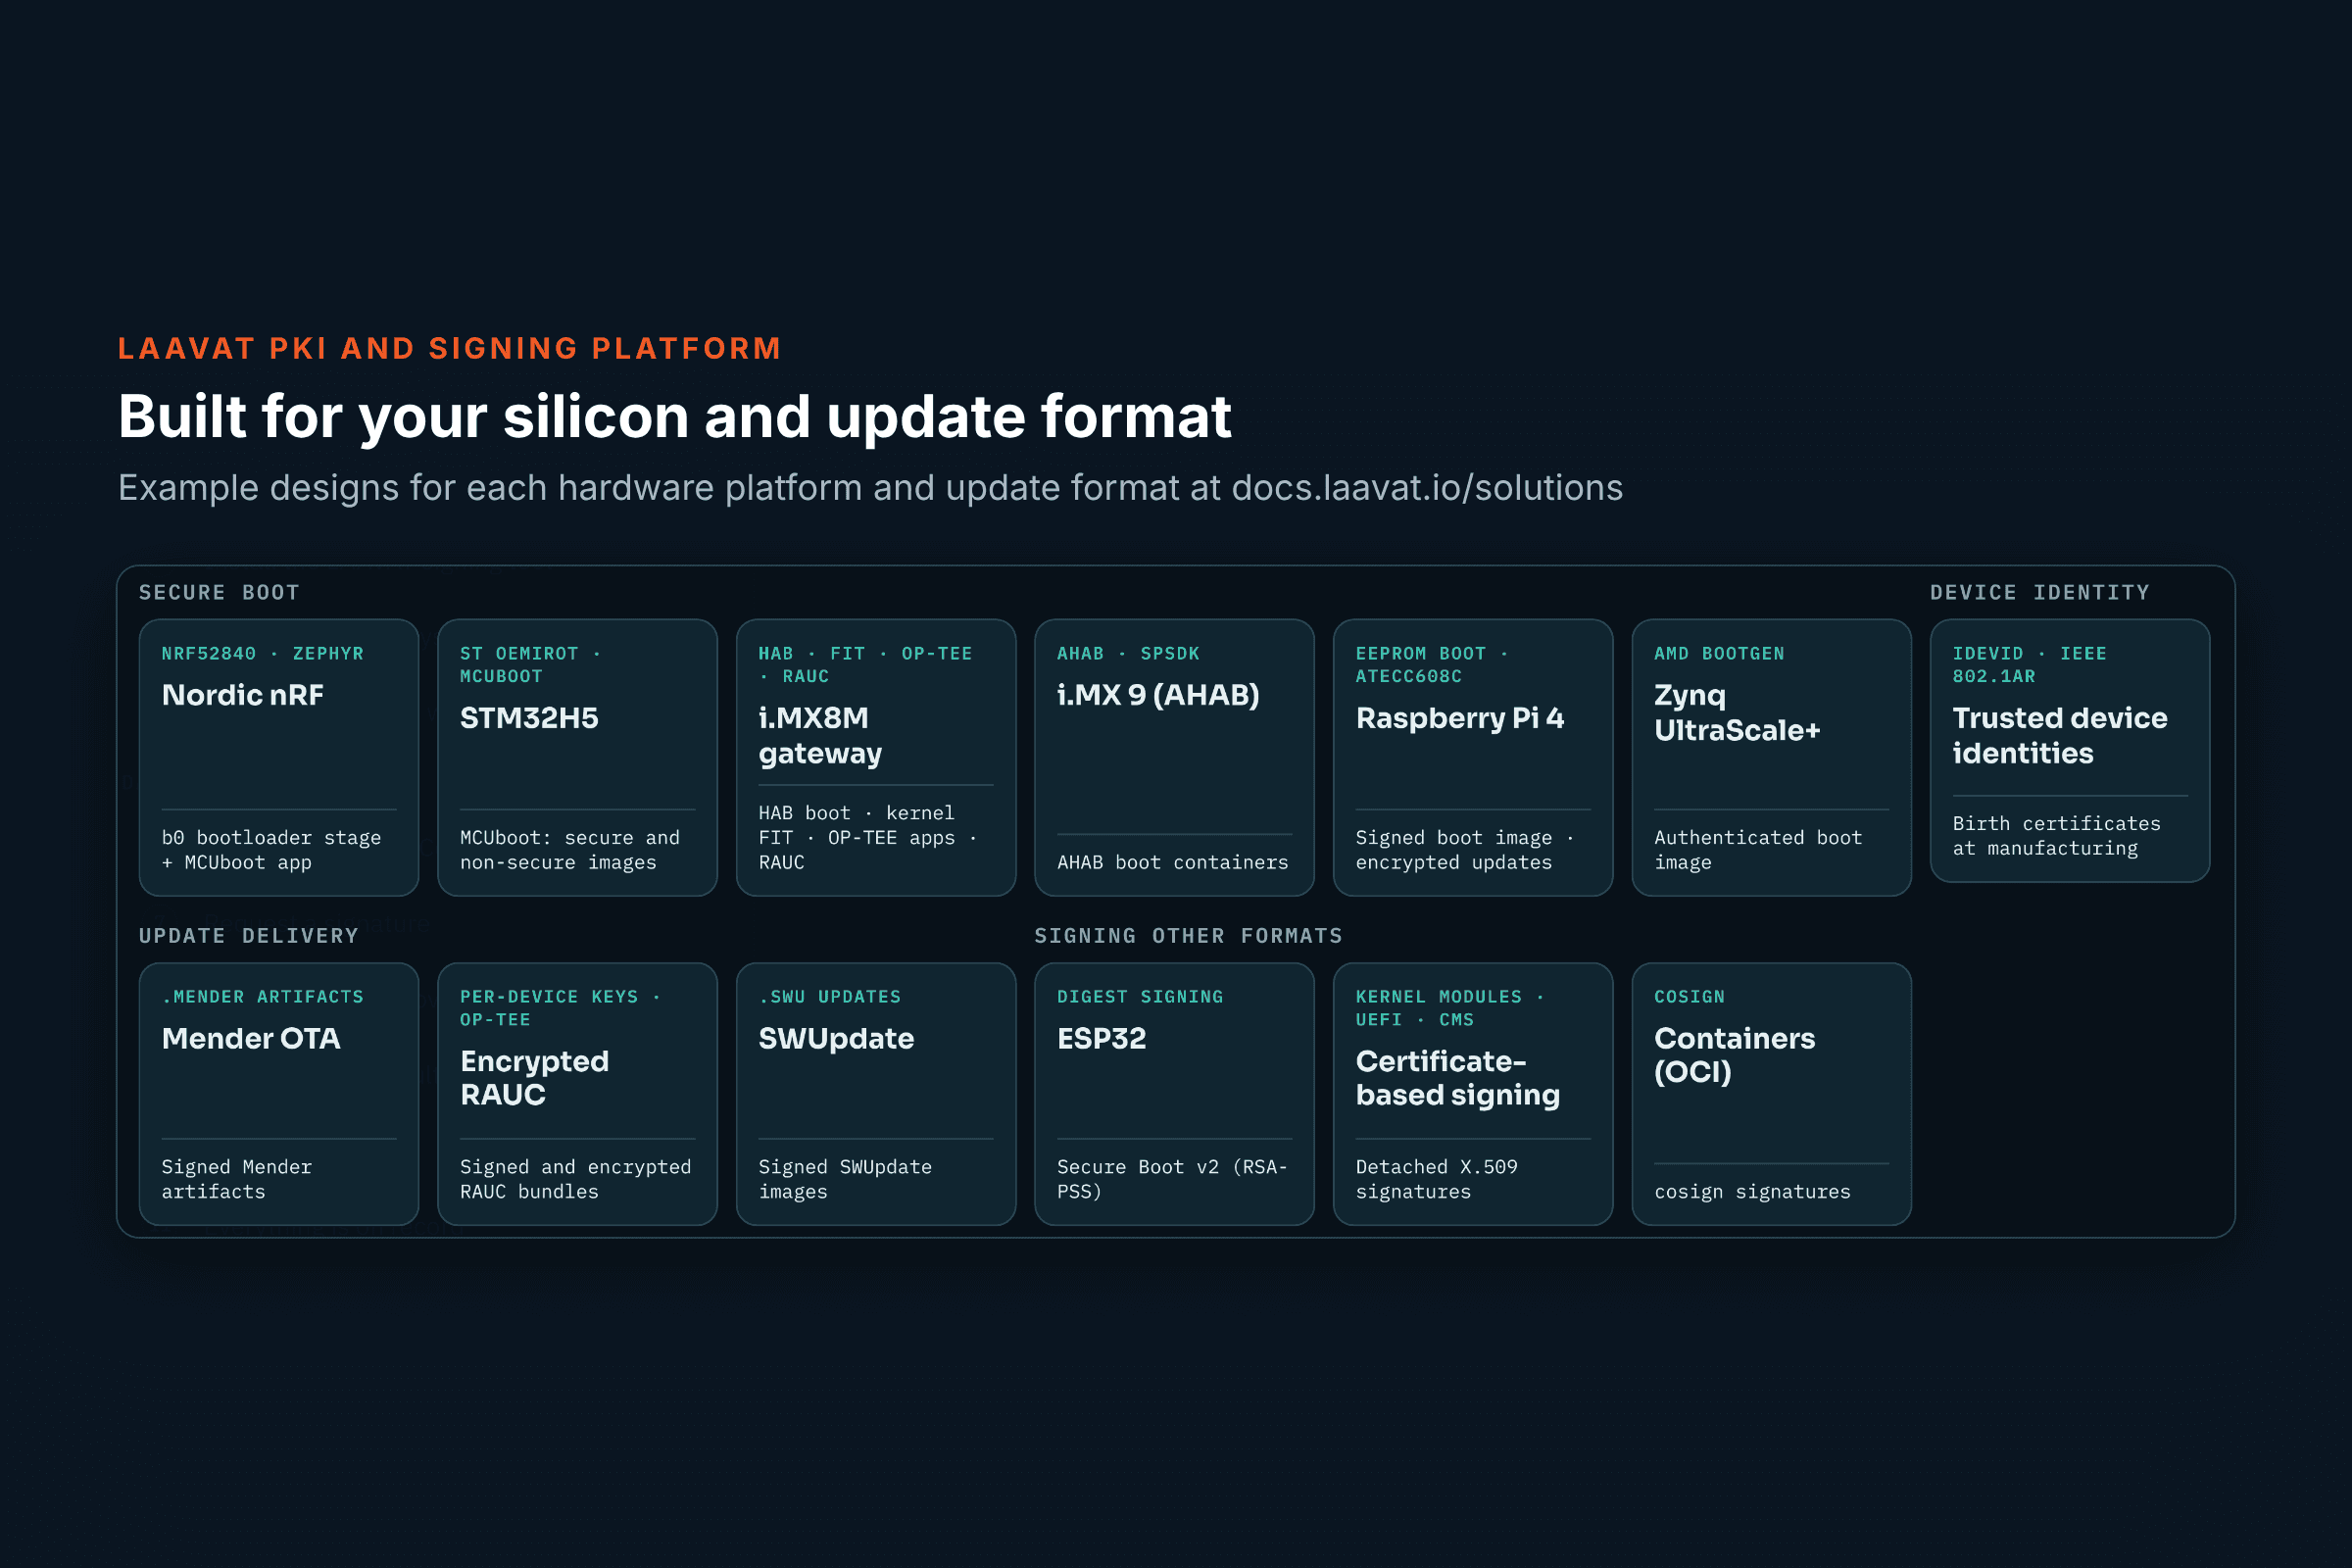
- Secure boot and update signing for NXP, AMD/Xilinx, TI, STM32, Nordic, Renesas, Microchip, ESP32, Raspberry Pi and UEFI
- Post-quantum ML-DSA and hybrid signing available today
Kategorien
Embedded Software für Datensicherheit (Security) Methoden & Werkzeuge für sichere Embedded Systeme
Produkt Information
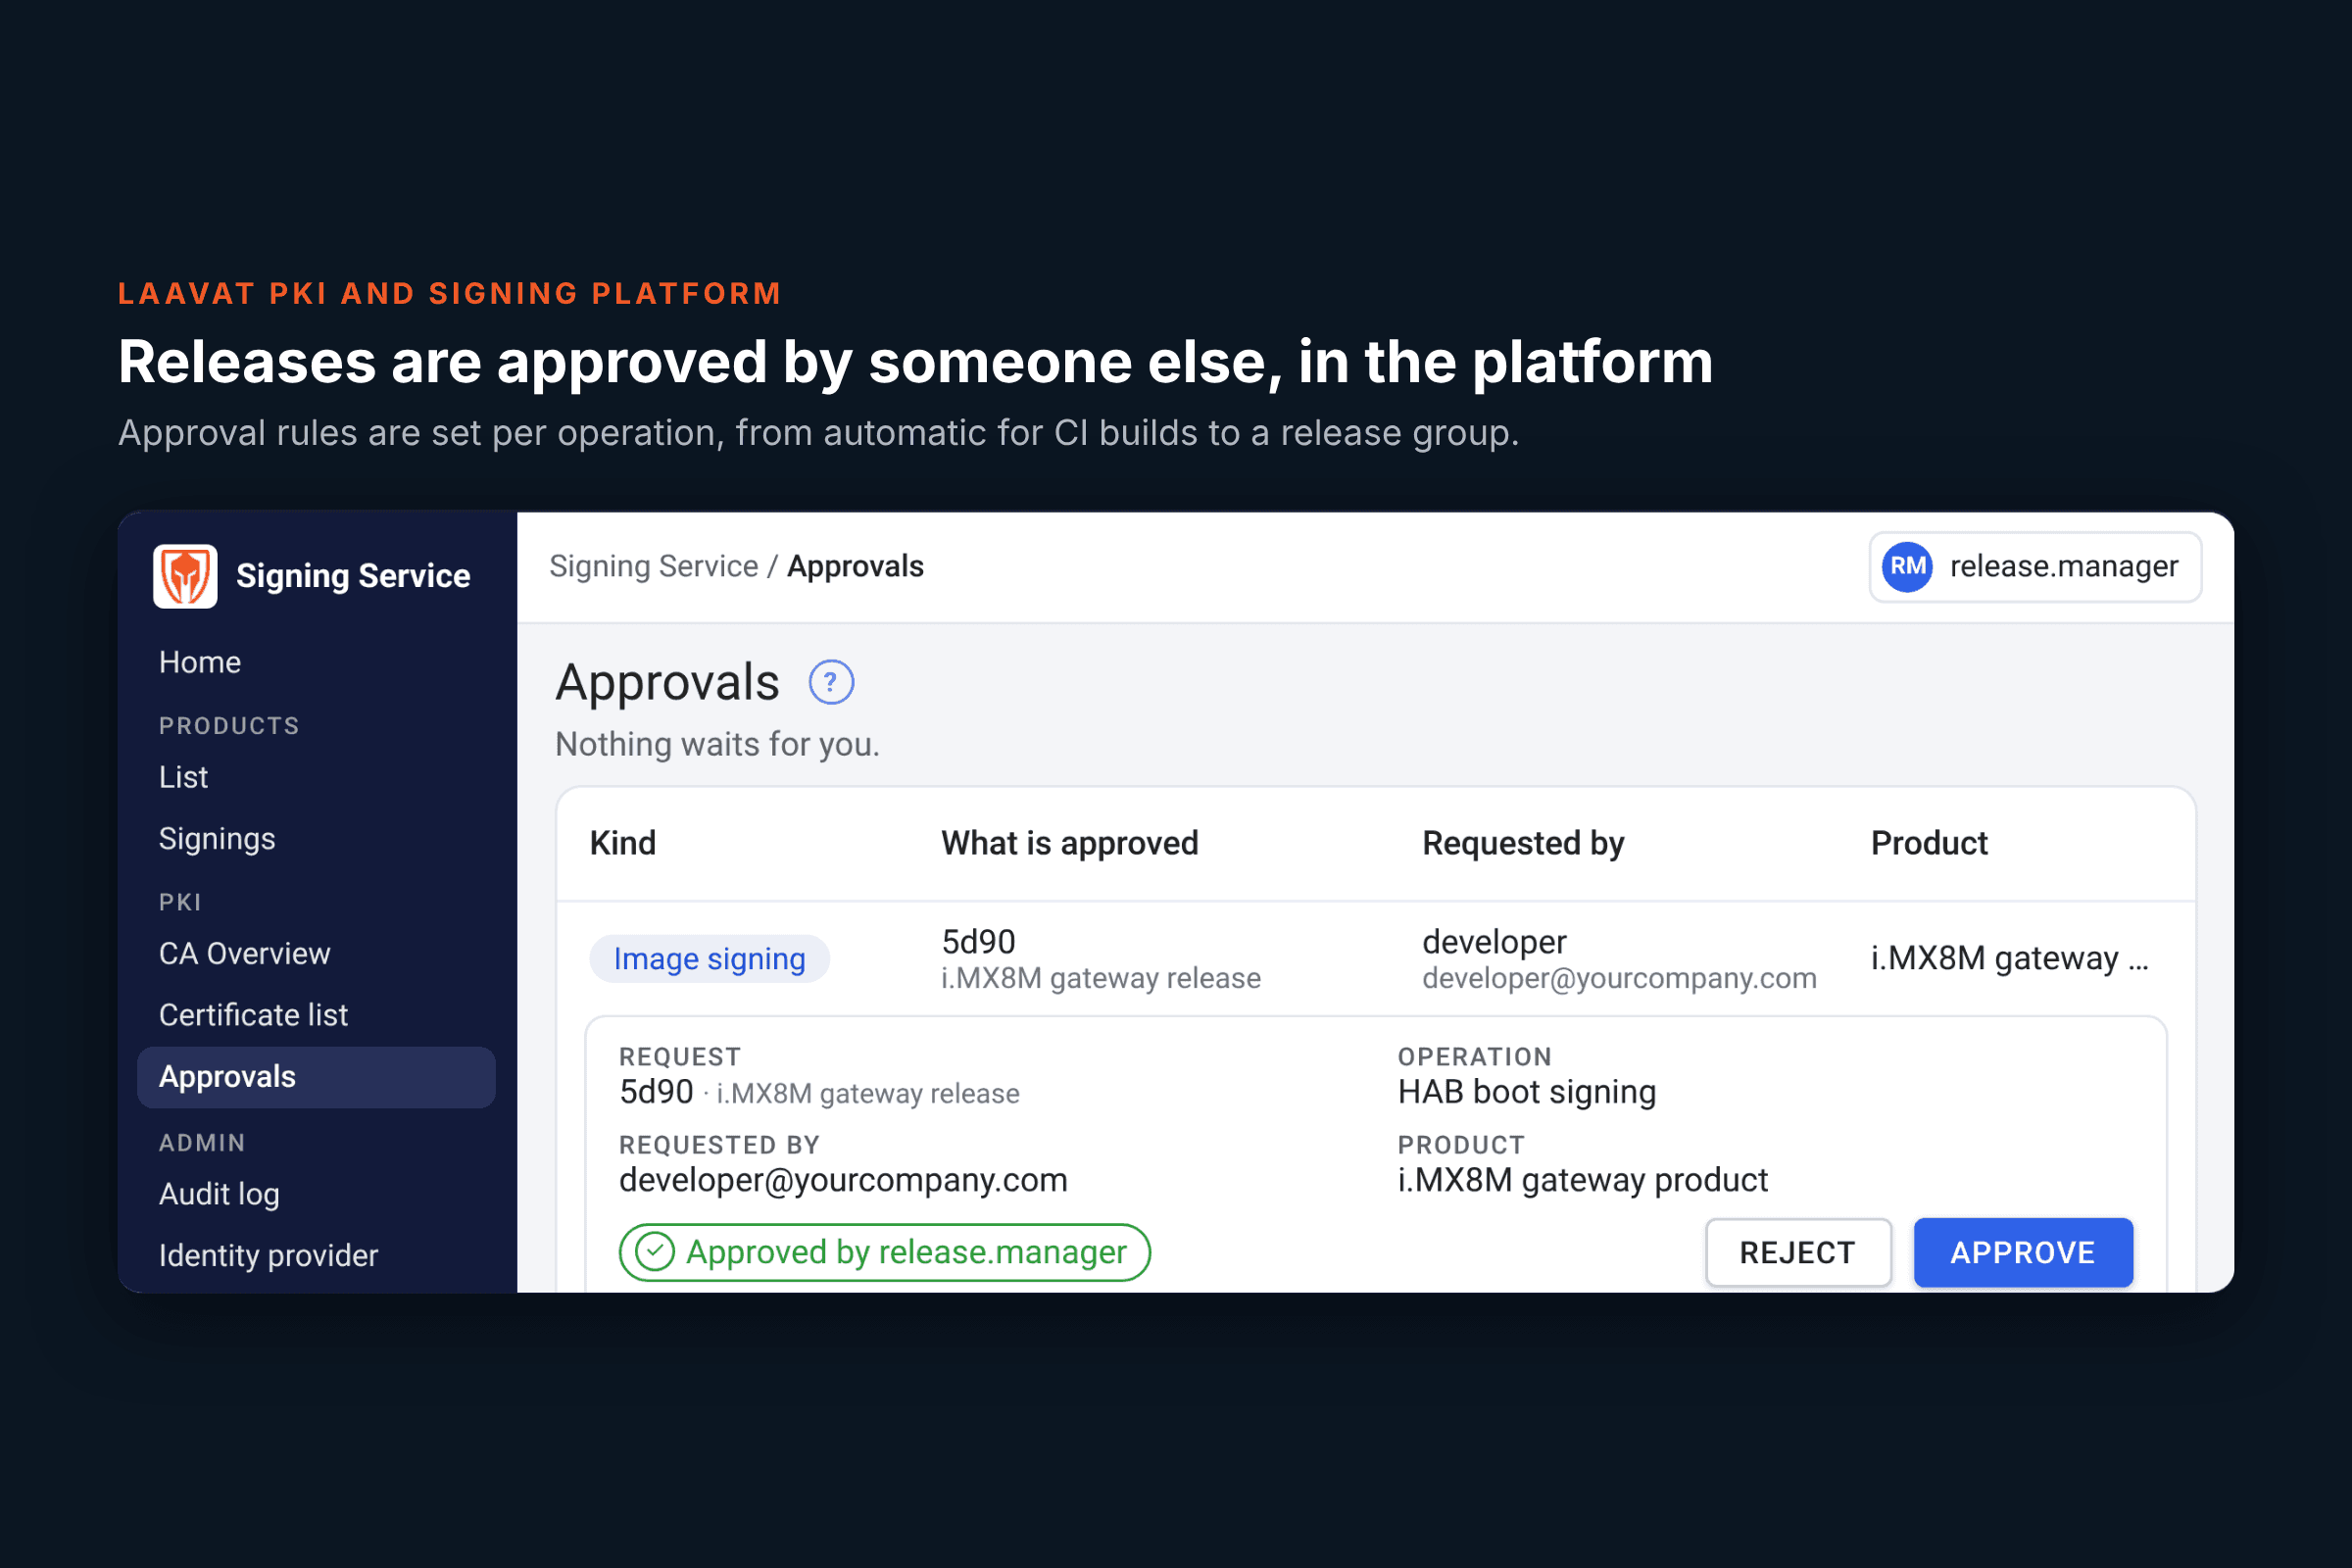
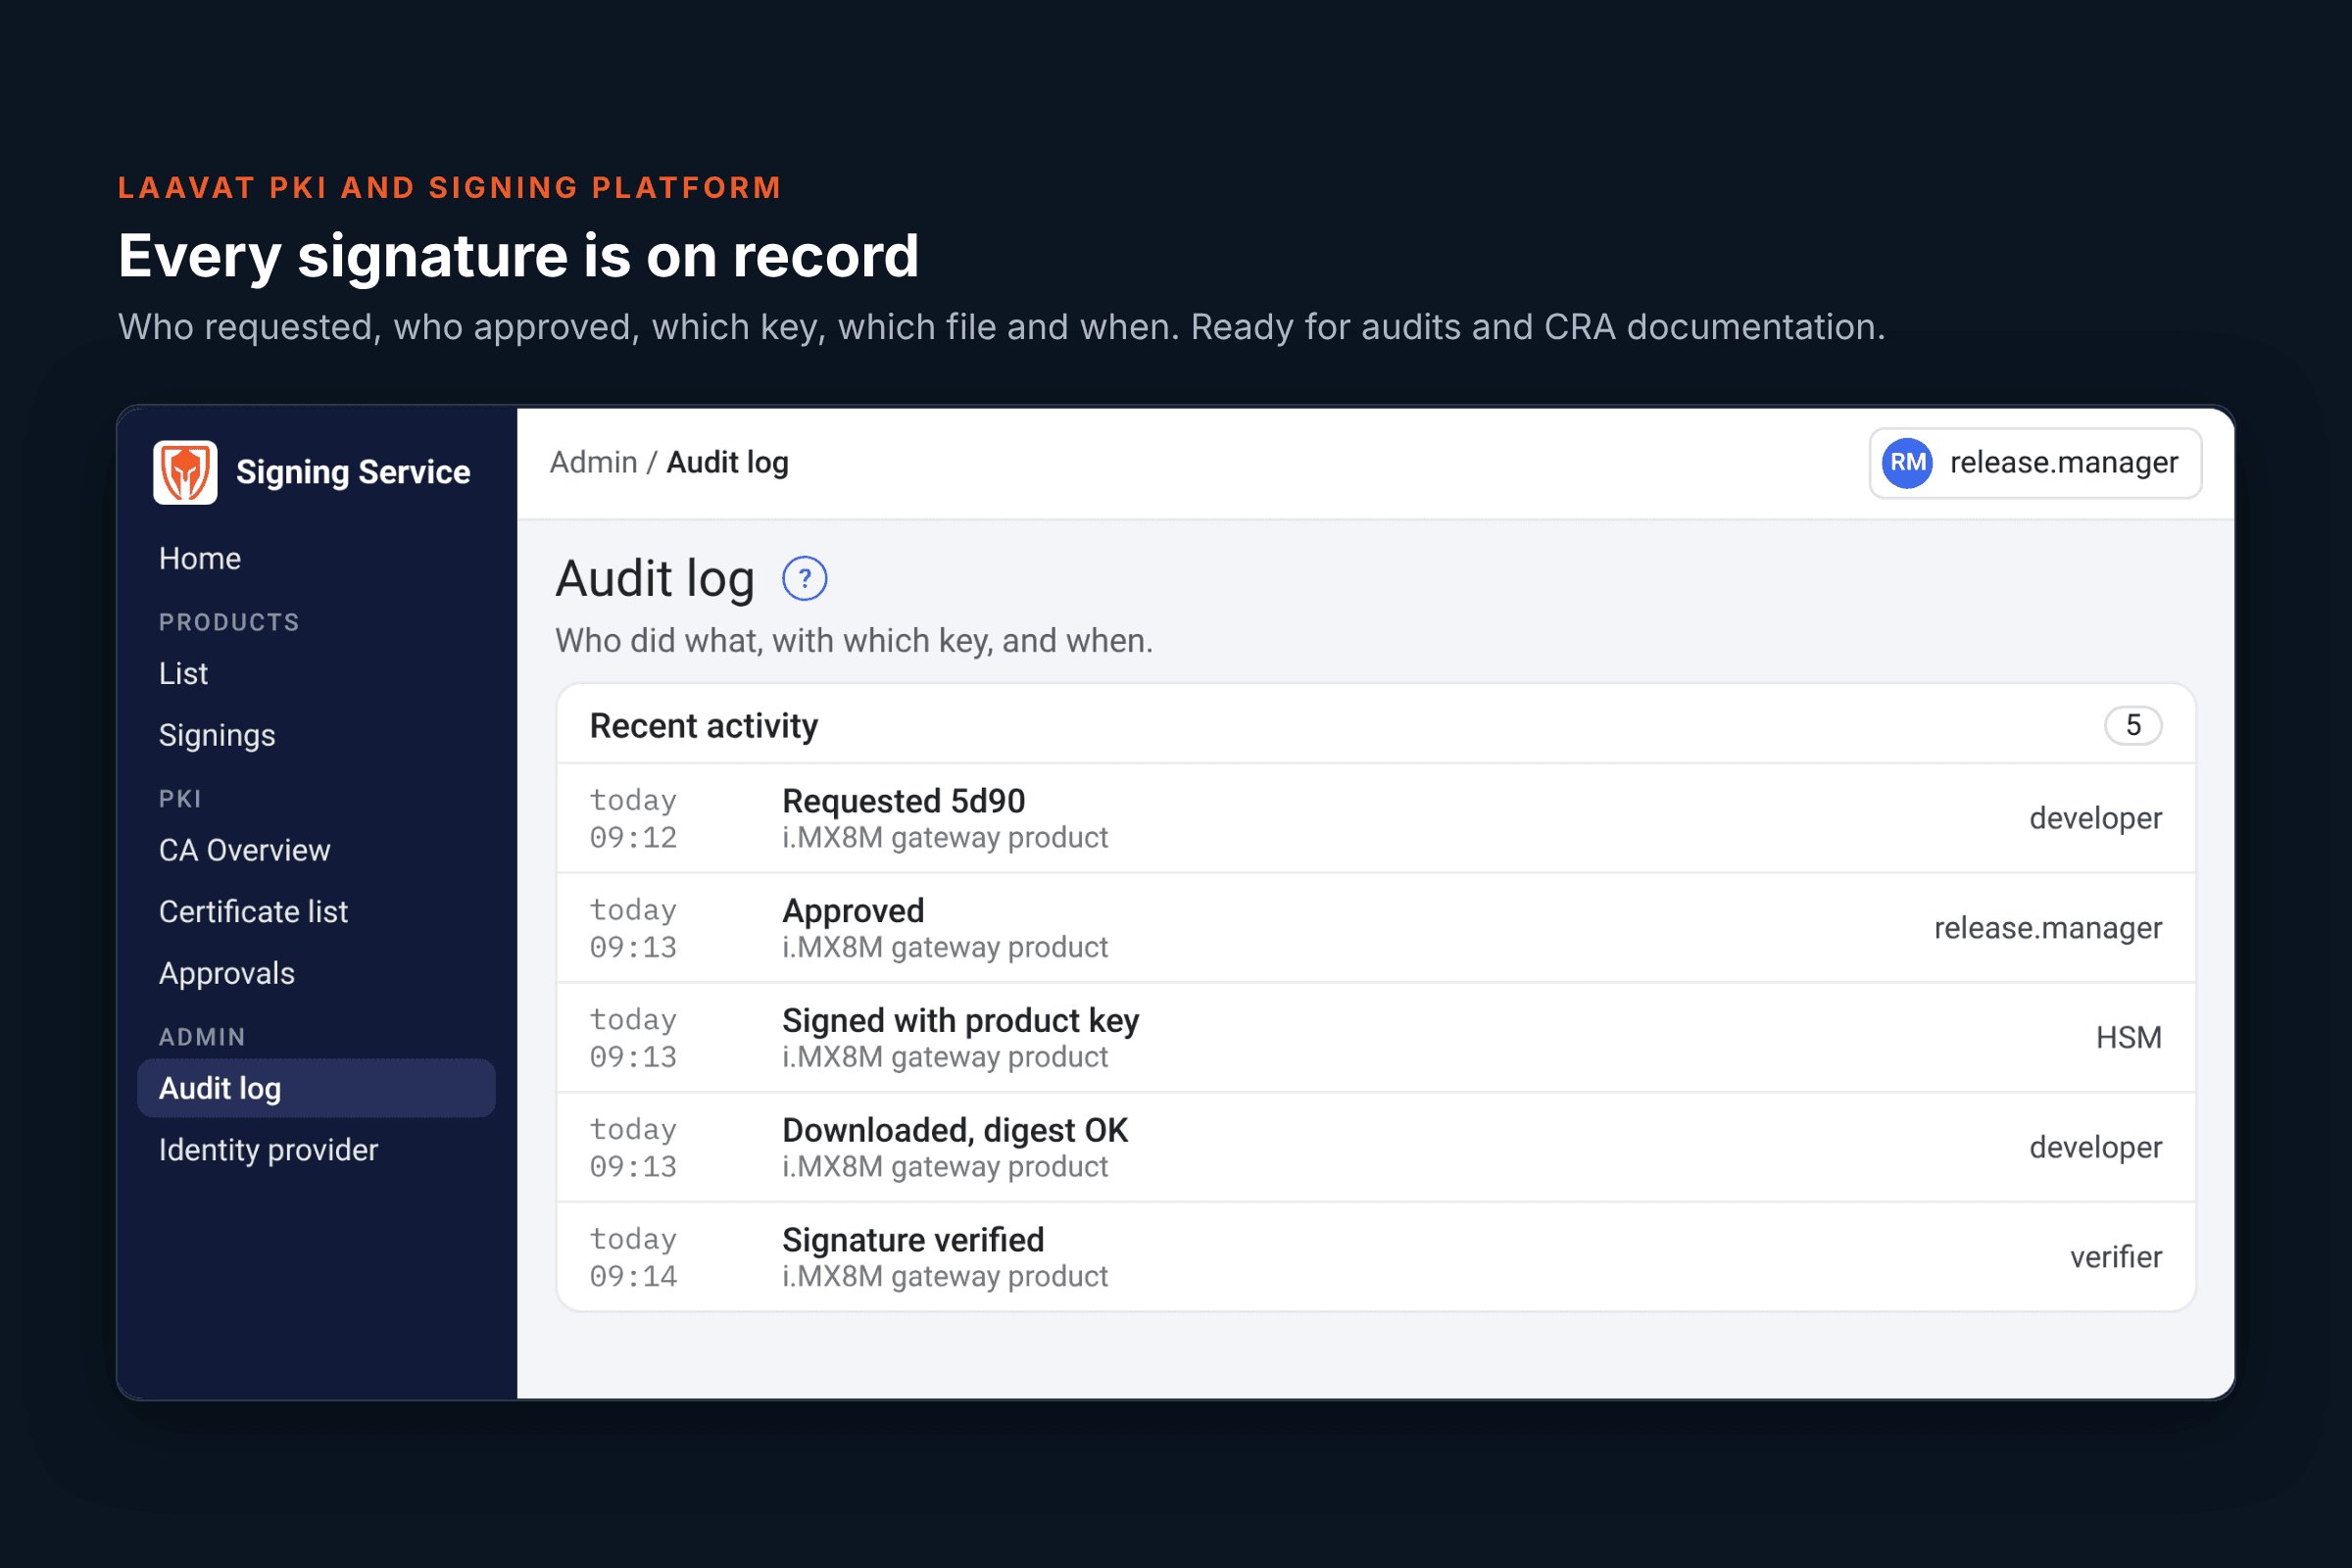
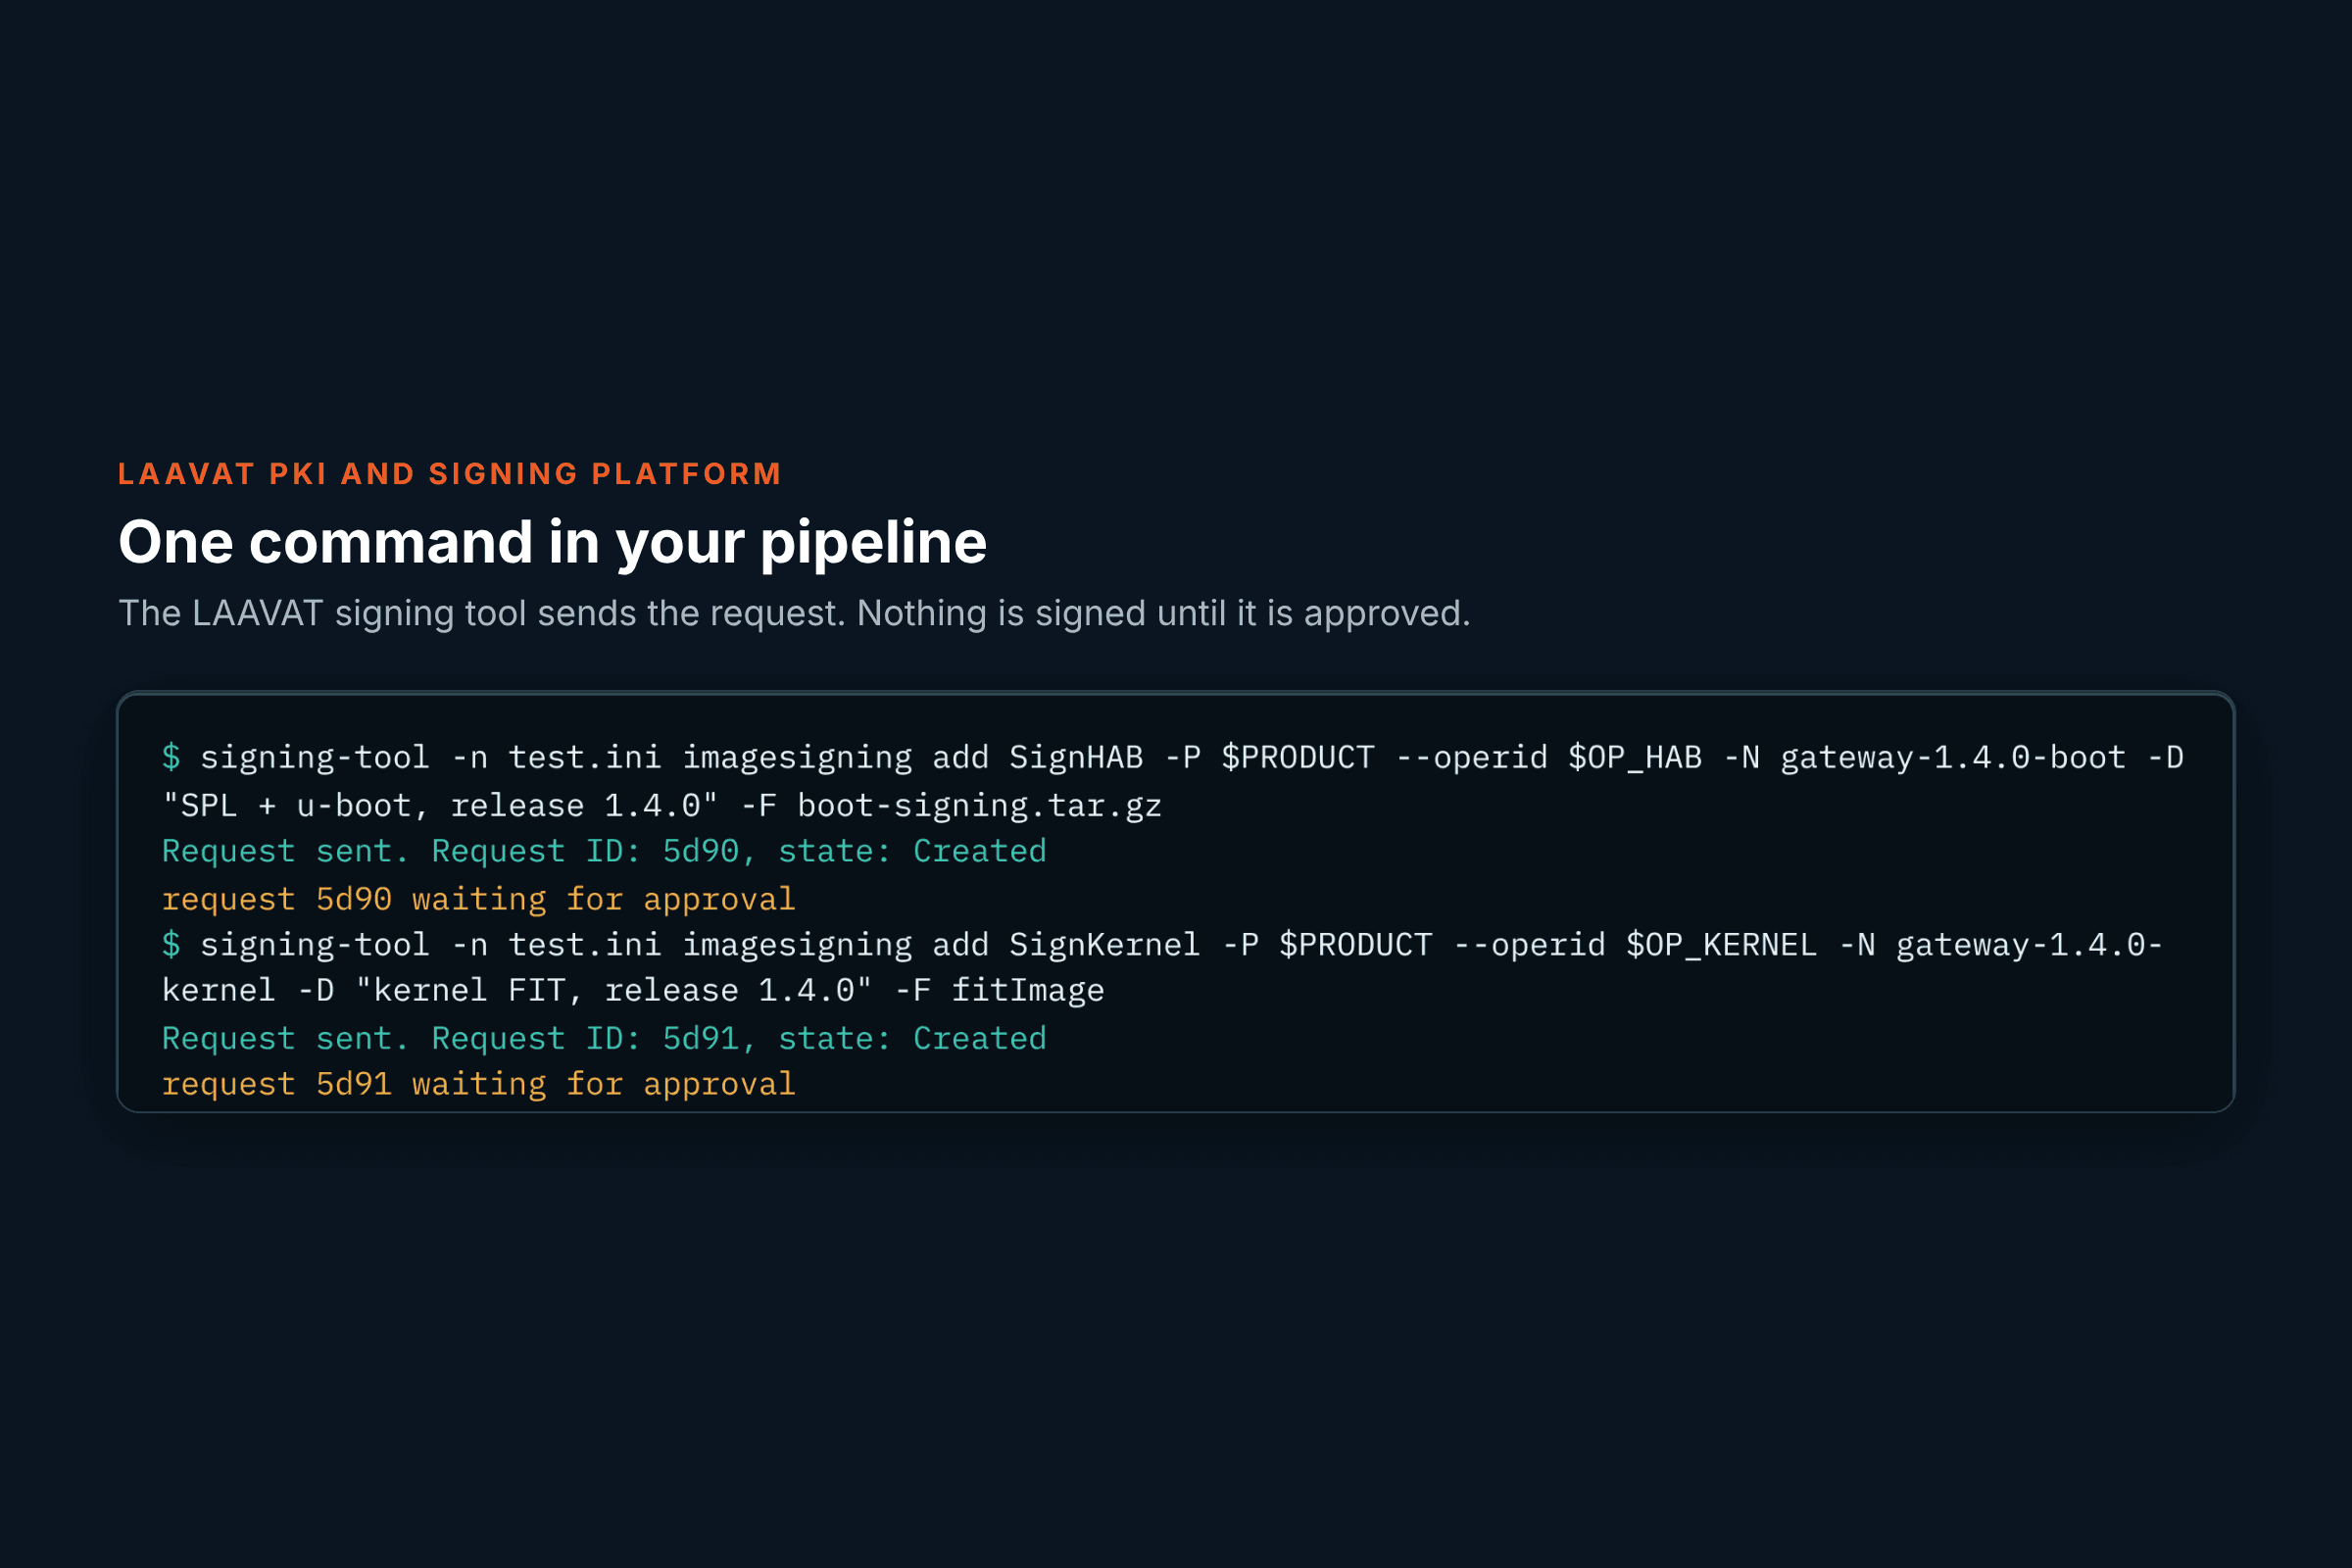
The LAAVAT PKI and Signing Platform gives embedded teams one service for secure boot signing, update signing, image encryption and device identity, managed from one web UI and REST API.
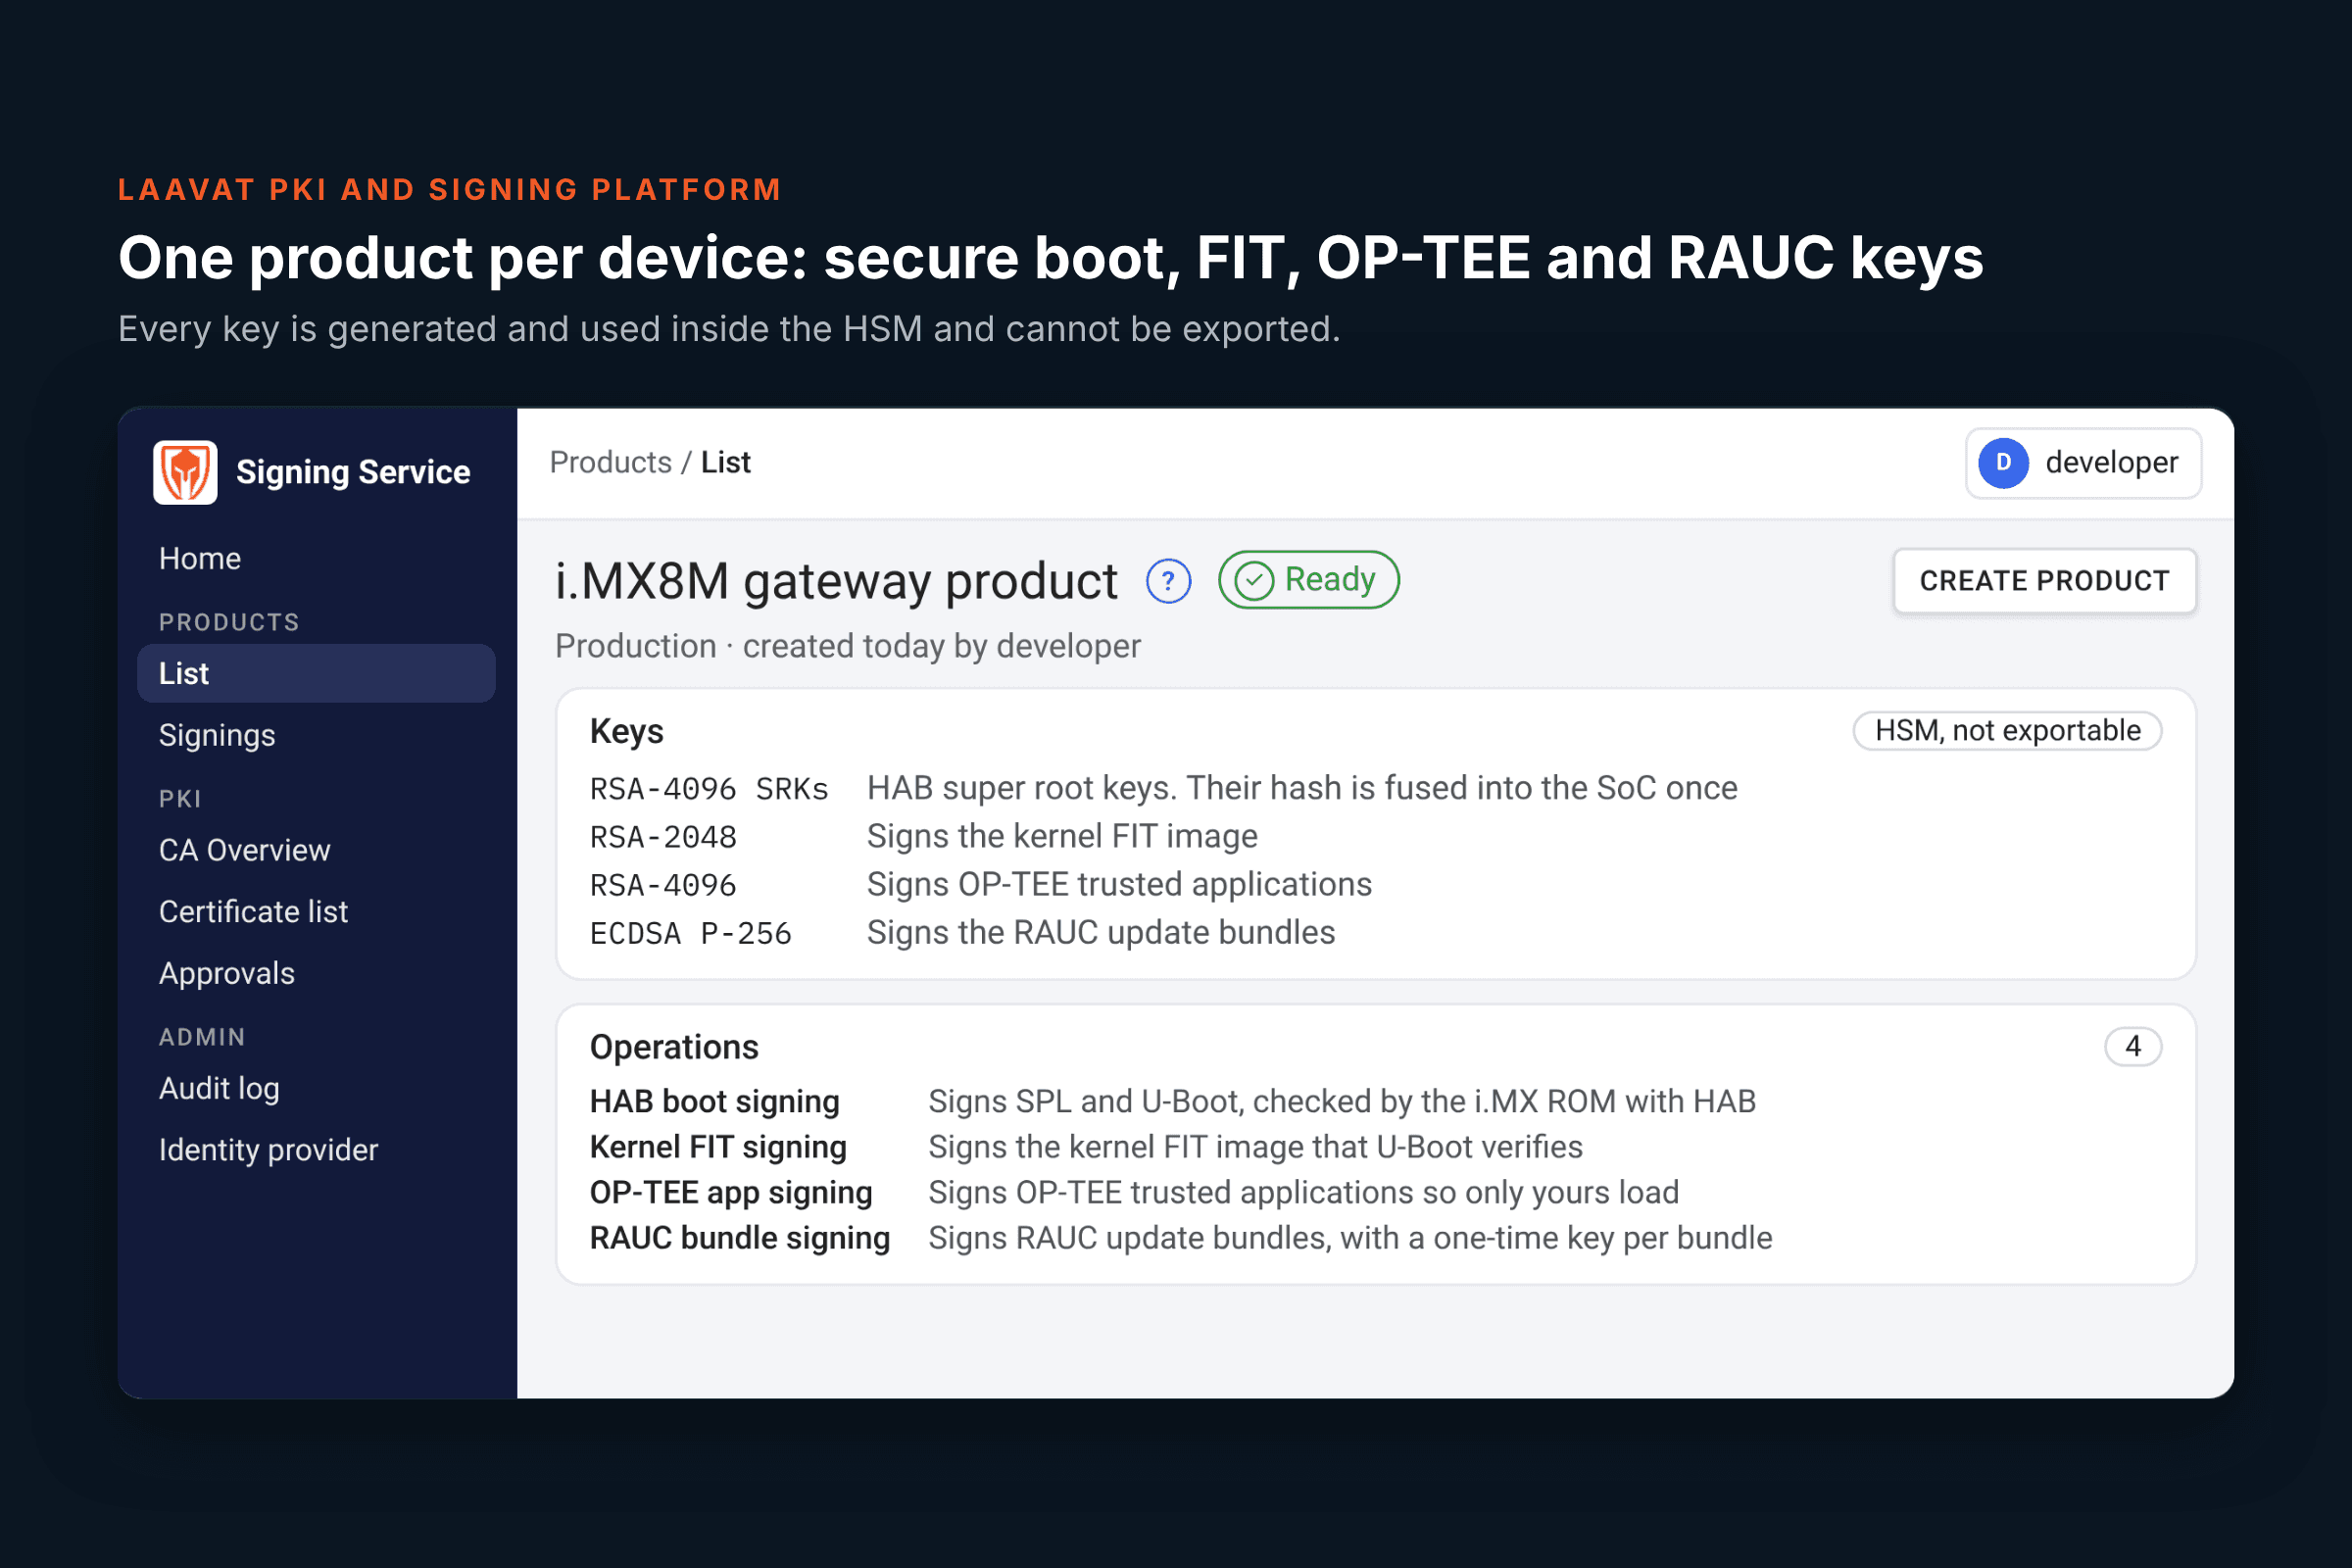
Secure boot: NXP HAB and AHAB, AMD/Xilinx Bootgen, Texas Instruments, Raspberry Pi, ESP32 and UEFI secure boot, plus MCUboot on STM32, Nordic, Renesas and Microchip.
Updates: signed FIT, RAUC (including encrypted bundles), Mender and SWUpdate. AES-GCM-256 image encryption with key delivery to manufacturing.
Device identity: CA hierarchies under your own or an existing root, IEEE 802.1AR IDevID at the factory over REST and LDevID in the field over EST, with ECC, RSA and ML-DSA chains.
Other signing: OP-TEE trusted applications, OCI container images, Windows binaries, kernel mo ...Download